08:00
REGISTRATION & REFRESHMENTS
08:50
WELCOME ADDRESS
09:00
FIRESIDE CHAT | The Current Threat Environment
A discussion on how today’s threat landscape is actively evolving, where defensive friction lies, and how these emerging threat vectors are directly translating into real-world insurance claims.
Panellists:
- Sydonie Williams, Head of International Cyber Risks, Beazley
- Matthew Broomhall, Cyber Information Security Officer, Lloyds of London
09:30
PANEL
AI Aggregation Risk – Realistic Disaster Scenario
Can current vendor risk management frameworks survive machine-speed exploitation, and if not, what replaces them?
- Where is the modelling community on second-tier concentrations – identity providers, CDNs, specific SaaS categories and how are portfolio managers adjusting line size ahead of the models catching up?
- What does machine-speed exploitation do to the patching assumptions underneath current underwriting, and what has materially changed at renewal?
- As aggregation concerns push towards named-peril framing, what does that do to the product for mid-market and SME buyers who need simplicity?
Panellists:
- Ed Pocock, Head of Cybersecurity, Gallagher Re
- Henry Skeoch, Cyber Portfolio Management Leader, Beazley
- Keith Nutburn, Account Executive, Arctic Wolf
10:15
From Threat Intelligence to Risk Intelligence
How $400 in stolen access can become a $5 million loss:
Access to a billion-dollar company can be bought on the dark web for around $400, and the warning signs often appear weeks before a claim. Using real underground evidence, honeypot data and cases from our cyber helpline, this keynote shows how attackers choose their targets, and how threat intelligence helps boards, decision makers and underwriters act before the loss.
By Mil Rajic , Head of Intelligence, DynaRisk
10:45
The Protection Gap: A Failure of Decision, or a Failure of Product?
This session pressures common explanations around the cyber protection gap.
- Is it a failure of decision-making that better analytics and advisory can close?
- How can we better educate the market on cyber risk and business resilience?
- Are buyers responding rationally to a product not yet trusted to pay at the scale and speed of today’s losses demand as cyber losses shift from data compromise toward operational disruption and sustained revenue impact?
Panellists:
- Lyndsey Bauer, Strategic Delivery Lead – Cyber, Miller Insurance
- Monica Tigleanu, Lead Underwriter – Cyber, MS Amlin
- Garrett Olson, Head of Insurance & Enterprise Risk Management, Wolt
11:30
NETWORKING BREAK
12:00
BREAKOUT WORKING SESSIONS
Cyber War Room Simulation
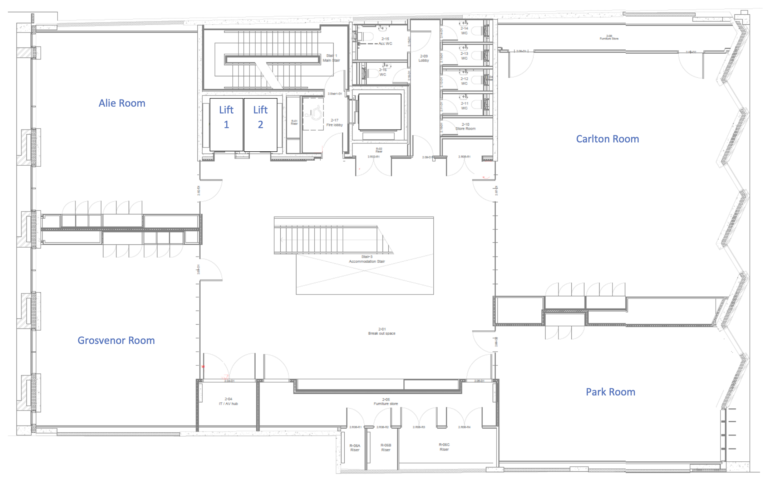
(Alie Room, floor 2)
This interactive session drops delegates into a live crisis scenario, moving from first alert to executive decision-making under real-time pressure. The scenario is authored with a threat intelligence analyst to ground it in current, real-world adversary behaviour, with Google Mandiant serving as the session’s intelligence partner.
Participants:
- Mathias Frank, Head of Incident Response, Mandiant UK & Ireland
Quantum Preparation Today
(Park Room, floor 2)
The question is what can the insurance industry do to help our policyholders prepare?
- Externally, should the carrier begin asking policyholders about their quantum plans and align with vendors to help them start the planning process?
- Internally: How does the carrier understand the risk they are willing to bear?
- How to harden systems and create a game plan for today and tomorrow’s quantum exposure.
Participants:
- Jason Curreri, General Counsel and Head of Wordings, Elpha Secure
- Vikas Patel, Cybersecurity Solutions Manager, Marsh
Cyber BI Claims: Friction, Reality and the Road Ahead
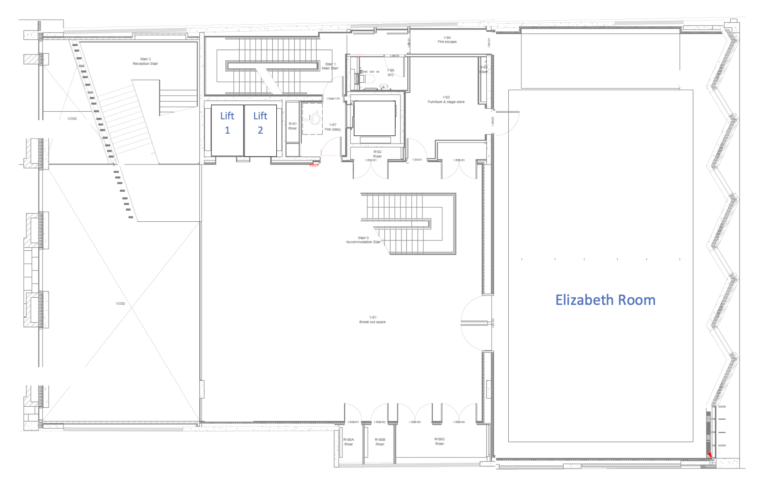
(Elizabeth room/main room, floor 1)
This session will explore some of the most challenging aspects of cyber business interruption claims, including common friction points in the claims process, the role of broker-appointed forensic accountants in preparing proofs of loss, and the ongoing debate around the concept of the “independent” forensic accountant.
The panel will also examine emerging issues that are becoming increasingly relevant to cyber BI claims, including the often-elusive timeline of contingent business interruption losses and whether growing reliance on AI could reduce an organisation’s ability to implement effective manual workarounds during a cyber incident.
Participants:
- Patrick Cannon, Global Head of Cyber Claims, Canopius
- Michael Milne, Investigative Accounting, Meaden Moore
Moderator:
- Jack Chamberlain, Deputy Class Underwriter – Cyber, Chaucer Group
Cyber Exposure Management – Aggregation Risk
(Grosvenor room, floor 2)
With portfolios growing and technical dependencies across companies becoming more complex, managing aggregation risk remains a major challenge.
In this discussion, we will focus on how to:
- identify accumulation potential and build an infrastructure inventory across the portfolio to detect concentrations,
- prioritise dependencies by ranking concentrations according to how critical and widely shared each dependency is, and
- map aggregation risk to insurance coverage by linking the prioritised exposures back to policies, limits, and treaty structures.
- Jonas Schwade, Managing Director, Cysmo
13:00
NETWORKING LUNCH
14:00
PANEL
Ransomware Economics: Who Pays If the Rules Change?
Mandatory economy-wide incident reporting is moving towards legislation. This session works through what that actually means for the cyber product.
- Where is coverage bending, and what does facilitation cover look like under a notify-and-pause regime?
- What happens to the threat-actor business model – do we see a shift to extortion-without-encryption, and is the policy ready for it?
- What is the operational reality for an insured covered by the ban when systems are down and the clock is running?
Moderator:
- Tom Egglestone, Head of Claims, International, Resilience
Panellists:
- William Finley, Senior Cyber Underwriter, QBE
- David Shluger, Head of Cyber Risk Advisory, Axis Capital
- Charlotte Wilson, Head Of Enterprise Business UKI, Checkpoint
14:45
DATA-LED PANEL
The Reckoning: The Claims Picture vs. The Narrative
The session opens with a data-led briefing on where losses are actually landing and coverage disputes are doing to the buyer relationship at the moment of claim.
Are enterprise risk functions and the insurance market developing a shared understanding of cyber risk or increasingly working from different pictures of the same threat landscape?
- What do recent claims trends reveal about the disconnect between risk perception and real-world loss drivers?
- How are coverage disputes at the time of a claim impacting long-term trust between buyers and carriers?
- What steps can enterprise risk functions and insurers take to align their technical understanding of evolving cyber threats?
Panellists:
- Josh Neary Gibson, Senior Underwriter – Cyber, CFC
- Ben Watson, Head of Cyber, Westfield Specialty
- Jimaan Sané, Head of Growth Cyber, Chubb
- Jelmer Andela, Global Commercial Director Cyber, Liberty Mutual
- Shrey Grover, UK Cyber Strategy Leader, Marsh
15:45
NETWORKING BREAK
16:15
POINT – COUNTERPOINT – THE BUYER-SIDE
What CISOs, CROs and GCs Need From the Cyber Insurance Market
The day’s closing set-piece: a buyer-side panel built around what cyber insurance needs to look like for enterprises operating at meaningful scale and complexity — a peer conversation to shape discourse on AI and cyber risk for the enterprise.
- On cyber and AI risk, what is becoming harder to explain and quantify with confidence, and where is the gap between what boards expect and what risk leaders can credibly deliver?
- Third-party risk — vendors, suppliers, partners and the AI systems embedded across them – how are you managing it in practice, and where are the limits of what’s manageable?
- Over the next 24 months, what’s the risk on your register you’re least confident the insurance market is set up to support?
Moderator:
- Jean Bayon de La Tour, Head of Cyber International, Howden
Panellists:
- Chiris Baetz, vCISO – Financial Services, Financial Conduct Authority
- Peter Downie, Chief Risk Officer, JLL
- Peter Kovacs, Head of Information Security and Data Privacy, nudge
17:10
CLOSING REMARKS
What the Room Has Worked Through
Drawing threads together across all in-the-round sessions: key tensions, emerging consensus, and what carries into the year-round programme for the Cyber Insurance Frontier community. Closing remarks to follow.
17:20
END OF CIF LONDON 2026
View Agenda
Venue MAP
FLOOR ONE
FLOOR TWO